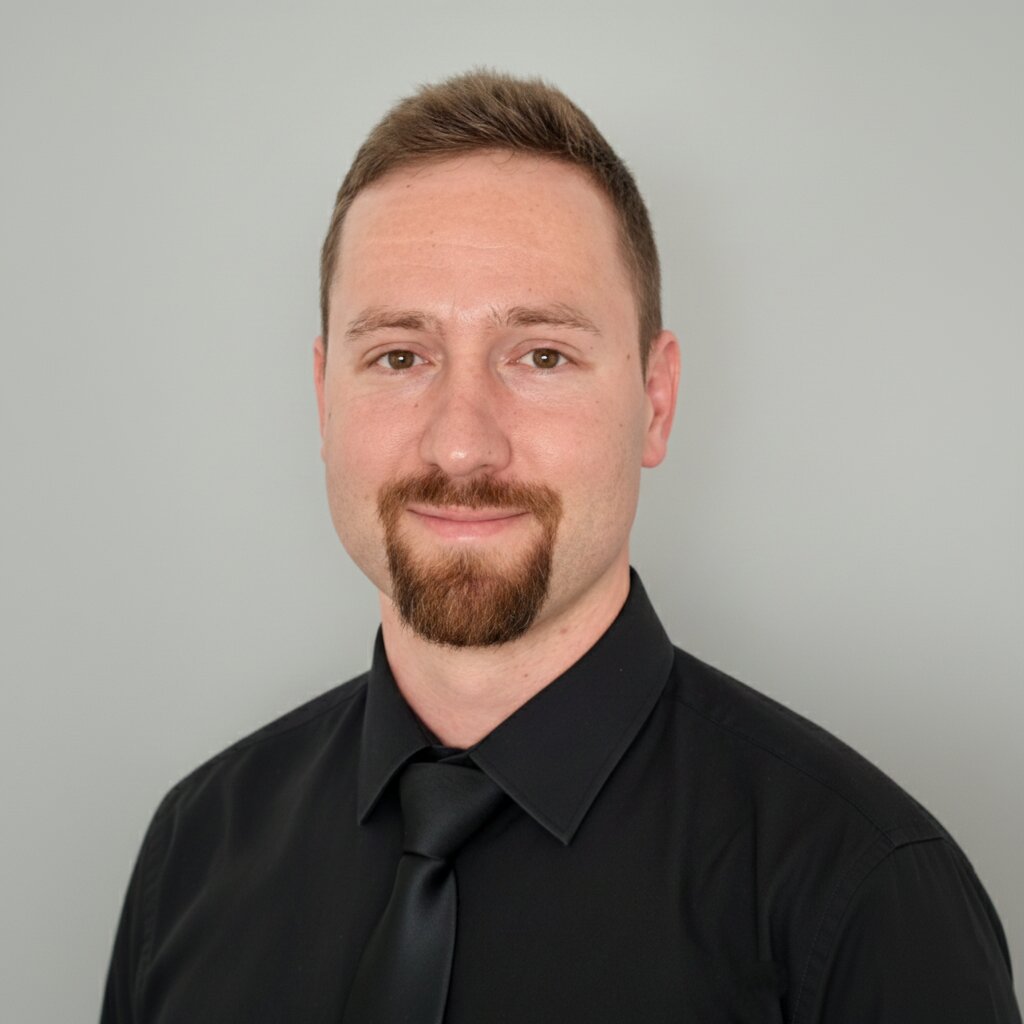
Portrait of Stiaan Terblanche
Available worldwide · RemoteAvailable on-site/hybrid · Western Cape, South Africa

Stiaan Terblanche

AWS Cloud Engineer · Cloud Security & AI

7 years running a retail business taught me that uptime, customer trust, and small failures that snowball are serious problems. Turns out, that's cloud engineering. Now I pair it with Cloud Security & AI that keeps humans in charge.

About

I learned ownership before I learned AWS

I spent 7 years running my own retail business and a nationwide e-commerce operation before making the leap into cloud. That experience taught me to solve real problems for real people under real constraints - budget, time, things breaking at the worst moment - and I bring that same ownership mindset to how I secure and automate cloud infrastructure.

I focus on Cloud Security and AI. My portfolio is real consulting scenarios, not isolated tutorials: least-privilege IAM, MFA for 100% of users, stored credentials replaced by short-lived OIDC roles, and Amazon Bedrock reviews where humans make the final call.

AI in the Cloud

Embedding intelligence into cloud-native pipelines

Automation

If it runs twice, it should run itself

Security

Threat-aware design across every layer

Architecting Solutions

Designing systems built to survive reality

Skills

The tools I reach for

A practical stack proven through hands-on, production-style builds, with security and AI at the core.

Cloud Security

Least-privilege access and hardened, defensible environments.

  • IAM Policy Design
  • Least Privilege
  • MFA Enforcement
  • GuardDuty
  • IMDSv2
  • Secrets Manager

AI in the Cloud

Bedrock-powered reviews and triage where humans make the final call.

  • Amazon Bedrock
  • PR Security Review
  • Template Triage
  • Incident Triage
  • Human-in-the-Loop

Infrastructure as Code

Repeatable, version-controlled infrastructure.

  • Terraform
  • AWS CDK
  • CloudFormation
  • TypeScript
  • Remote State

DevOps & Automation

CI/CD pipelines with short-lived credentials and tested rollback.

  • GitHub Actions
  • CI/CD
  • OIDC
  • Reusable Workflows
  • Tested Rollback

Containers

Packaging and orchestrating workloads reliably.

  • Docker
  • ECS
  • Fargate
  • Service Connect
  • ECR Scanning

Observability & Monitoring

Making systems measurable, diagnosable, and resilient.

  • CloudWatch
  • Container Insights
  • Alarms
  • Health Checks
  • Failure Testing

Cloud Platforms

AWS core services for building secure, scalable, and resilient infrastructure.

  • EC2
  • S3
  • VPC
  • ALB
  • RDS
  • CloudFront
  • Route 53

Serverless

Event-driven automation and usage-based data stores.

  • Lambda
  • EventBridge
  • SNS
  • Aurora Serverless v2
  • DynamoDB

Architecture & Migration

Modernising legacy infrastructure into resilient, cost-aware AWS architectures.

  • Multi-AZ Design
  • Three-Tier
  • Legacy Modernisation
  • Microservices
  • Well-Architected
  • ADRs

Projects

Selected cloud work

A few builds that show how I approach architecture, migration, and security on AWS.

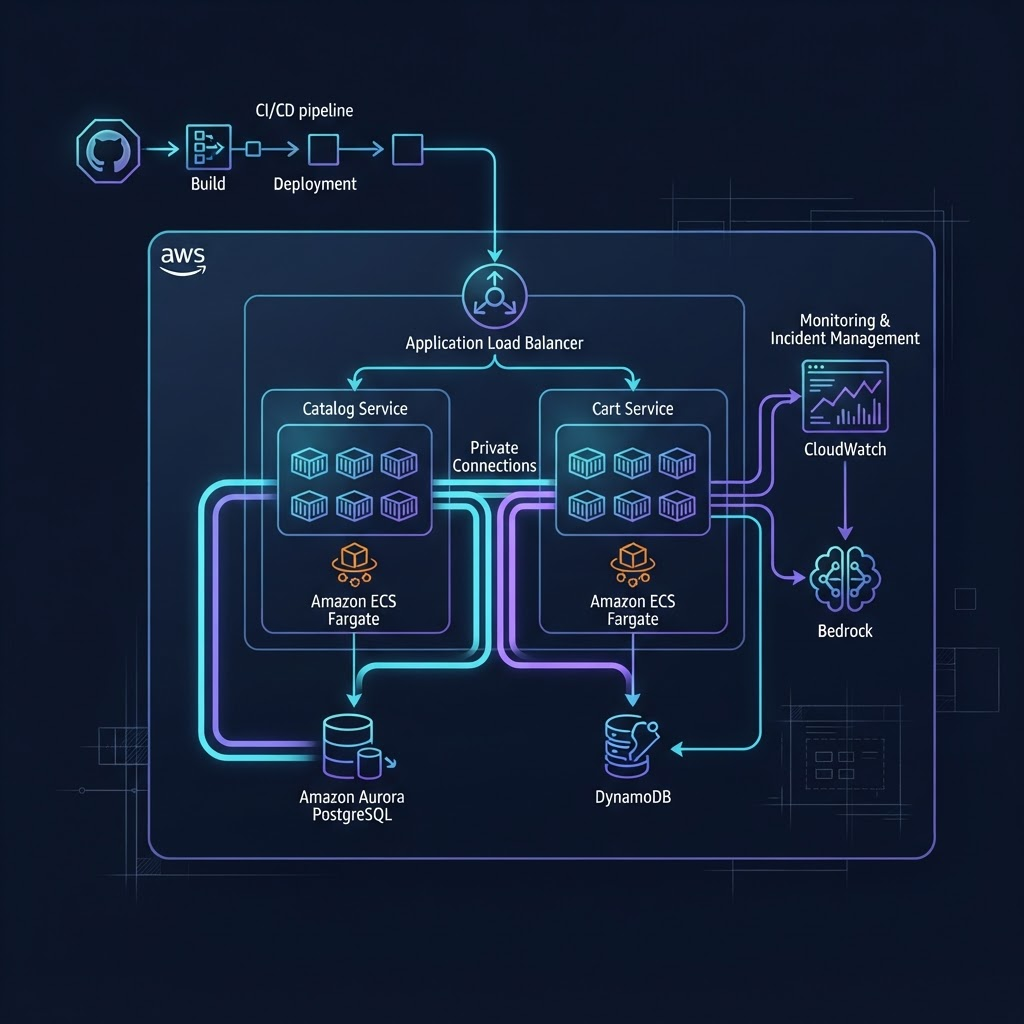
ShopMesh Containerized Microservices architecture visualization
Microservices & Containers

ShopMesh Containerized Microservices (opens GitHub repository)

Transformed a catalog-and-cart monolith into independently deployable Node.js services on ECS Fargate, with Aurora PostgreSQL, DynamoDB, private ECS Service Connect communication, OIDC-based GitHub Actions delivery, and CloudWatch-to-Bedrock incident triage.

  • Node.js
  • Docker
  • ECR
  • ECS
  • Fargate
  • Aurora Serverless v2
  • DynamoDB
  • Service Connect
  • GitHub Actions
  • CloudWatch
  • Bedrock
  • SNS
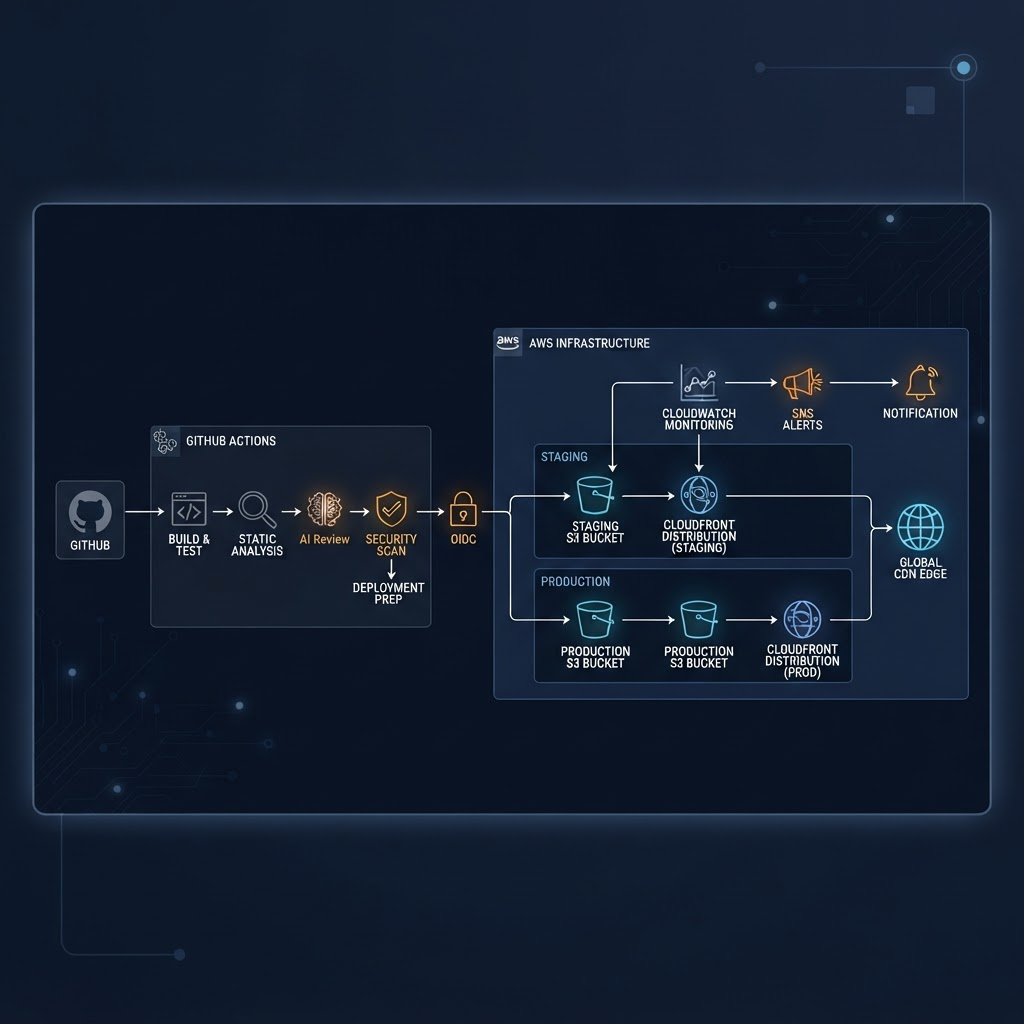
CloudPipe CI/CD Automation architecture visualization
DevOps & Automation

CloudPipe CI/CD Automation (opens GitHub repository)

Built a secure AWS CI/CD platform with CDK, GitHub Actions, OIDC authentication, isolated staging and production environments, S3 versioned rollback, CloudFront delivery, CloudWatch and SNS monitoring, and a non-blocking Amazon Bedrock pull-request review.

  • AWS CDK
  • GitHub Actions
  • CI/CD
  • OIDC
  • S3
  • CloudFront
  • CloudWatch
  • SNS
  • Lambda
  • Bedrock
Cloud Engineering Portfolio Website architecture visualization
Web Platform & AI

Cloud Engineering Portfolio Website (opens GitHub repository)

Designed and deployed an architecture-led cloud engineering portfolio with Next.js, structured TypeScript content, GitHub-connected Vercel delivery, a Markdown-grounded AI Architecture Guide using Vercel AI Gateway and Qwen, and an anonymous Resend contact path with server-side validation.

  • Next.js
  • React
  • TypeScript
  • Vercel
  • AI Gateway
  • Resend
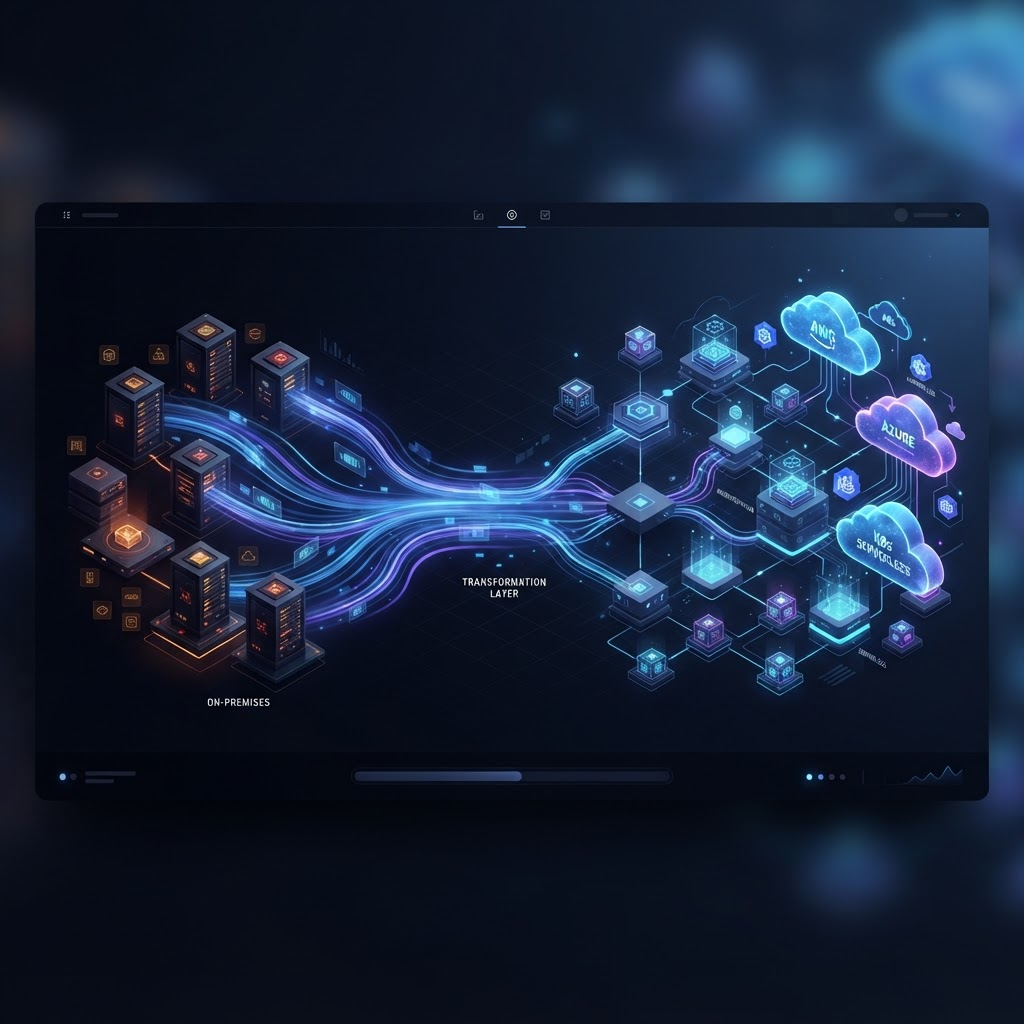
TechHealth Inc. AWS Infrastructure Migration architecture visualization
Cloud Migration

TechHealth Inc. AWS Infrastructure Migration (opens GitHub repository)

Moved manually managed healthcare infrastructure toward an auditable AWS platform with AWS CDK and TypeScript. Redesigned the environment as a two-AZ, three-tier architecture with public ALB and web layers, private app and Multi-AZ RDS tiers, layered security groups, Secrets Manager credentials, Auto Scaling Groups, and SSM administration without SSH. Added an event-driven S3, EventBridge, Lambda, Bedrock, and CloudWatch pipeline to review synthesized CloudFormation templates for security risks.

  • AWS CDK
  • TypeScript
  • VPC
  • EC2 Auto Scaling
  • ALB
  • RDS
  • Bedrock
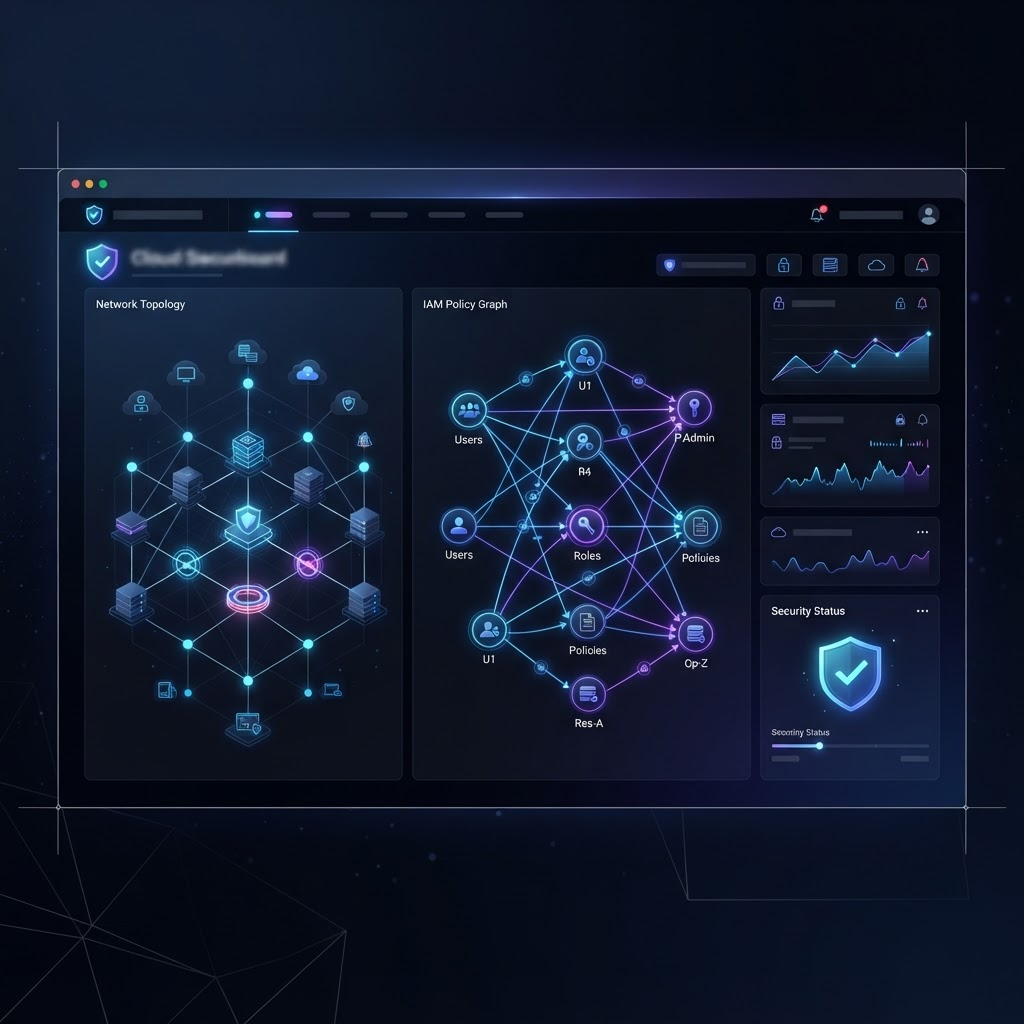
StartupCo Security Refactor architecture visualization
Cloud Security

StartupCo Security Refactor (opens GitHub repository)

Refactored StartupCo’s AWS security baseline by hardening root access with MFA, introducing role-based IAM groups and least-privilege permissions, codifying the environment in Terraform, and validating the live state through incremental imports and plan reviews. The project also documents a future-ready multi-AZ target architecture with GuardDuty, CloudWatch, private application and database tiers, and layered network controls.

  • Terraform
  • IAM
  • MFA
  • GuardDuty
  • CloudWatch
  • AWS Architecture
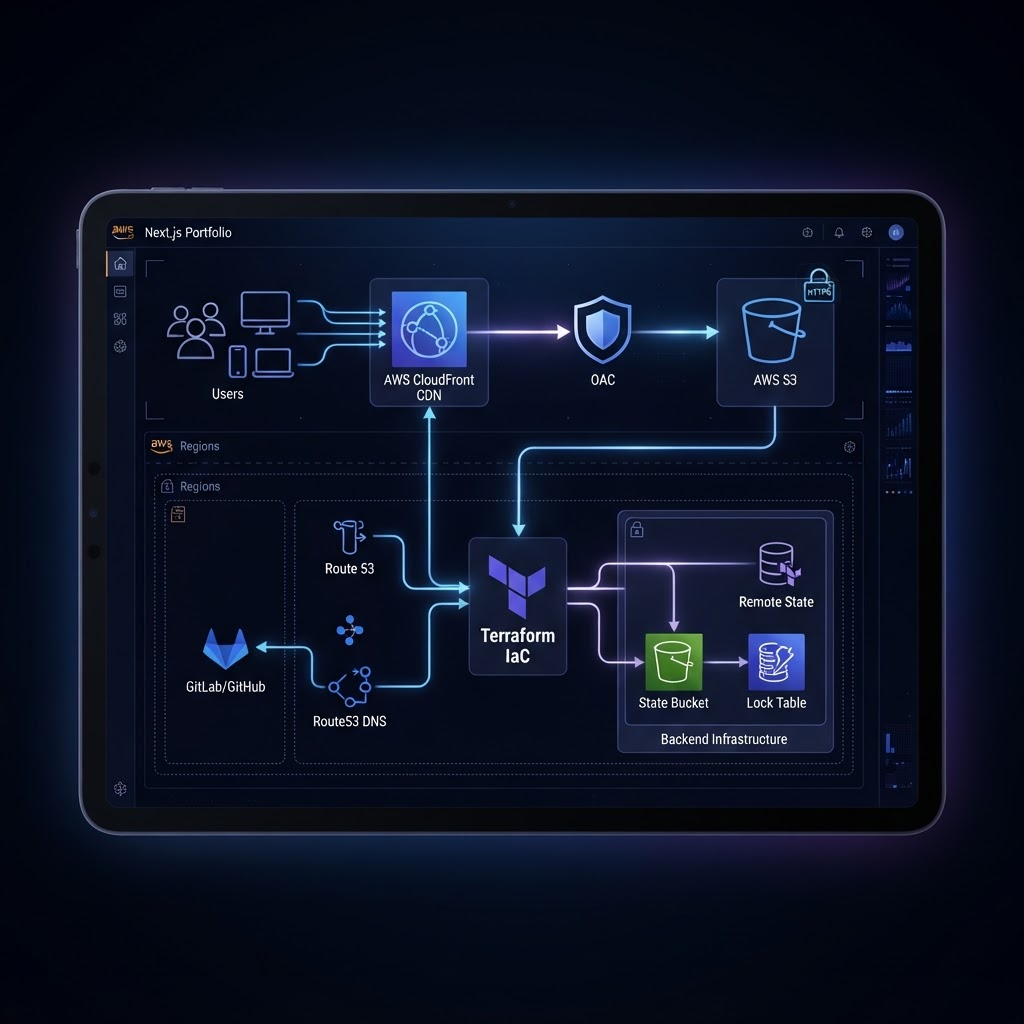
Terraform Portfolio Deployment architecture visualization
Infrastructure as Code

Terraform Portfolio Deployment (opens GitHub repository)

Deployed a statically exported Next.js portfolio to AWS using Terraform-managed infrastructure. Built a secure CloudFront and S3 architecture with Origin Access Control, HTTPS, blocked public bucket access, global content delivery, and remote Terraform state with S3 native locking for safe, repeatable operations.

  • Terraform
  • S3
  • CloudFront
  • OAC
  • Remote State
  • Next.js

Experience

Where I've worked (Tech & Cloud relevant)

  1. Cloud Engineer · Cloud Engineering Academy

    Jul 2025 — Present
    • Enforced least-privilege security across projects with role-based IAM, MFA for 100% of users, IMDSv2, layered security groups, private encrypted data stores and Terraform-defined GuardDuty, hardening 50+ AWS resources and cutting IAM baseline provisioning by 87% (about 2 hours to 15 minutes).
    • Eliminated stored AWS credentials from CI/CD by using short-lived OIDC roles in GitHub Actions, and automated staging-to-production delivery to replace 15-20 minute manual releases, proven across 56 workflow runs and 11 pull requests.
    • Built 3 Bedrock-powered AI integrations (PR security review, template security triage, incident triage), including a non-blocking PR reviewer (8 PRs, 0 false positives) and a template pipeline that flagged 2 of 4 failing checks on its first run, with humans making the final decision.
    • Replaced unnoticed downtime with automated detection and response using CloudWatch alarms, EventBridge, Lambda, SNS, Bedrock-assisted triage and a 5-minute site health check, validated through deliberate failure and rollback tests on live infrastructure.
    • Migrated a healthcare-style workload to AWS with CDK/TypeScript across 2 Availability Zones (VPC, ALB, Auto Scaling, private Multi-AZ RDS, Secrets Manager), cutting environment creation by about 94% (4 hours to 15 minutes) and codifying 50 infrastructure and 20 security-pipeline resources as repeatable IaC.
    • Re-architected a coupled monolith into ECS Fargate microservices (Aurora Serverless v2, DynamoDB) that scale independently on 70% CPU targets, communicate privately via ECS Service Connect, and roll back automatically, using a single NAT gateway across 2 AZs (50% fewer than the default layout).
    • Documented security and cost-versus-risk trade-offs for every project, such as deferring AWS WAF (~$5/month plus ~$1/rule) and rejecting unneeded RDS read replicas, in decision logs, ADRs and architecture diagrams.
  2. Co-Founder & Owner · Prime Growth Nutrition

    Jul 2018 — Jun 2025
    • Co-founded and scaled a nutrition retailer from a single brick-and-mortar store into a nationwide e-commerce business with a dedicated warehouse, mobile app and external marketplace channels. Strong first-year revenue from launch, 209.19% growth in Year 2, and 5.25x overall growth by Year 5 (51.4% CAGR), with roughly 75% of sales via digital channels.
    • Migrated the website from Shopify to WooCommerce to improve SEO, customisation and backend integration for the South African market. Ran a 28-plugin stack covering payments (PayFast & Stripe online, Yoco in-store), courier rates (Bob Go), product search (FiboSearch), reviews and loyalty points, and kept 301 redirects in place with Redirection.
    • Automated order processing, stock sync, batch and expiry tracking, scheduled sales, reporting and email marketing (MailPoet, cart-abandon recovery, review-request flows), saving 20-25+ hours per week and avoiding additional hires, which kept operating costs lean and protected margins.
    • Managed 1000+ SKUs across 30+ suppliers and 3-5 courier partners at any time, using sales and stock data to time supplier orders for cash flow and cutting higher-priced overseas brands in favour of better-fitting local ranges.
    • Drove paid acquisition through Google Shopping product feeds (Product Feed Pro/Elite), with Google Tag Manager and pixel tracking to measure traffic, on-site behaviour and ad performance. This fed continuous customer-experience improvements and earned 100+ 5-star Google reviews.
    • Kept the business resilient with scheduled automated backups of the site, backend and data (Backuply), hosting and DNS uptime alerts plus manual checks, and a backend that kept processing orders and customer communication through front-end outages, so manual order capture was rarely needed.
    • Launched mobile apps for both store generations: Shopney on Shopify, then AppPresser and its AppCommerce suite on WooCommerce, connected through the WordPress REST API with custom development.

Contact

Let's build something on the cloud

Have a migration, an architecture problem, or a role in mind? Send a note and I'll get back to you.